VERITY / SECURITY EVIDENCE CONTROL
Operational security posture, measured from evidence.
Read the estate you already run. Score the standards you are held to. Expose failed sources, stale readings and unassessed controls before they reach the board.
READ-ONLY WHERE SUPPORTED
DEPLOYMENT: ONE AFTERNOON
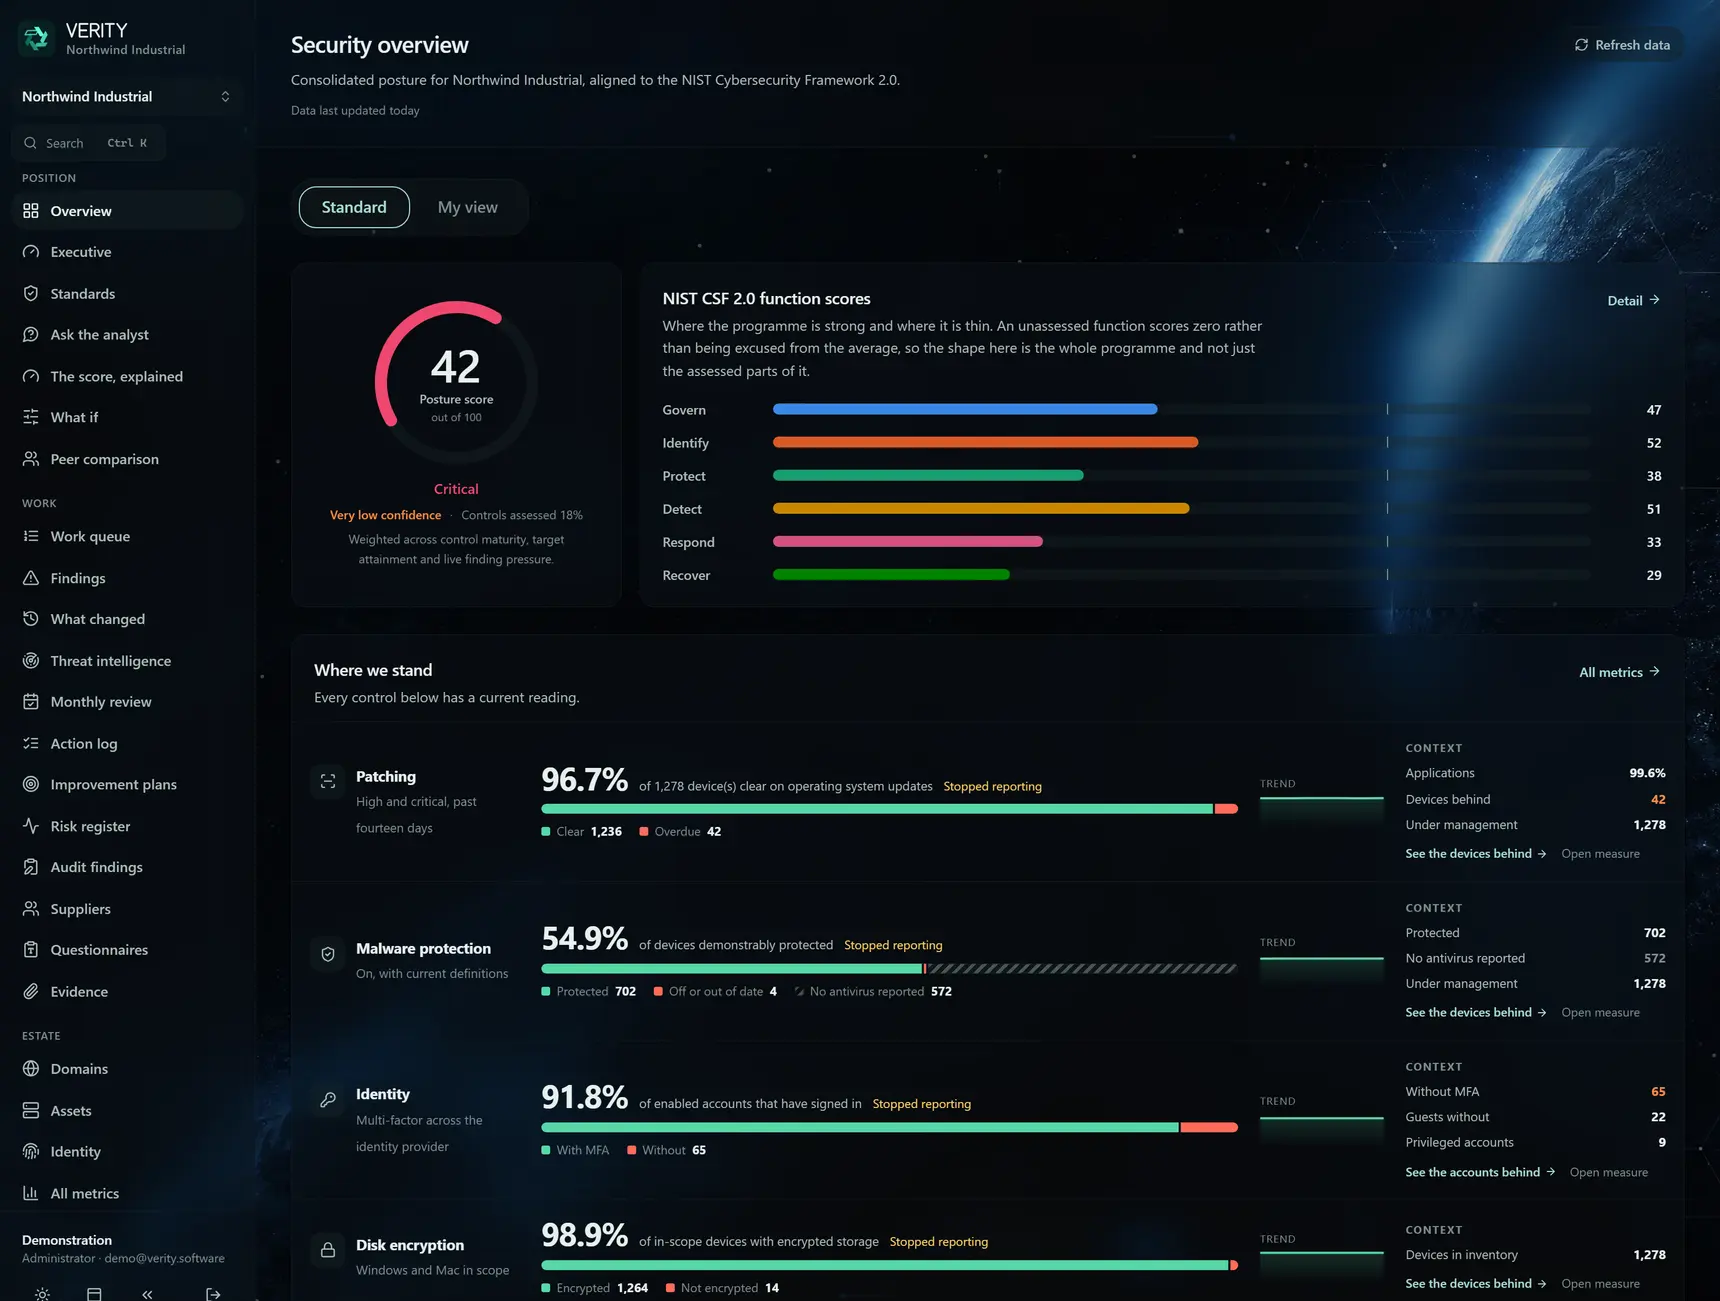
Built for security leaders and service providers who have to explain risk clearly, act on it, and prove the work was done.
01 / EVIDENCE
A posture score is only useful when the evidence survives scrutiny.
Verity keeps the source, age and coverage of every measure attached to the result. A missing reading stays missing. A failed connector stays visible. Your team can explain the number without rebuilding it in a spreadsheet.
02 / WORKFLOW
One evidence base. Four useful outcomes.
Connect each source once. Verity normalises the evidence and carries it through to reporting, readiness and remediation.
- 01Collect
Read your security tools, documents and passive checks.
- 02Measure
Map the evidence to a defined registry of security measures.
- 03Assess
Score posture and readiness using versioned rules.
- 04Act
Prioritise findings and publish the right report for each audience.
THE PRODUCT, IN USE
Move from evidence to action without losing the source trail.
Each view is a real Verity screen using sanitised demonstration data.
OBSERVE
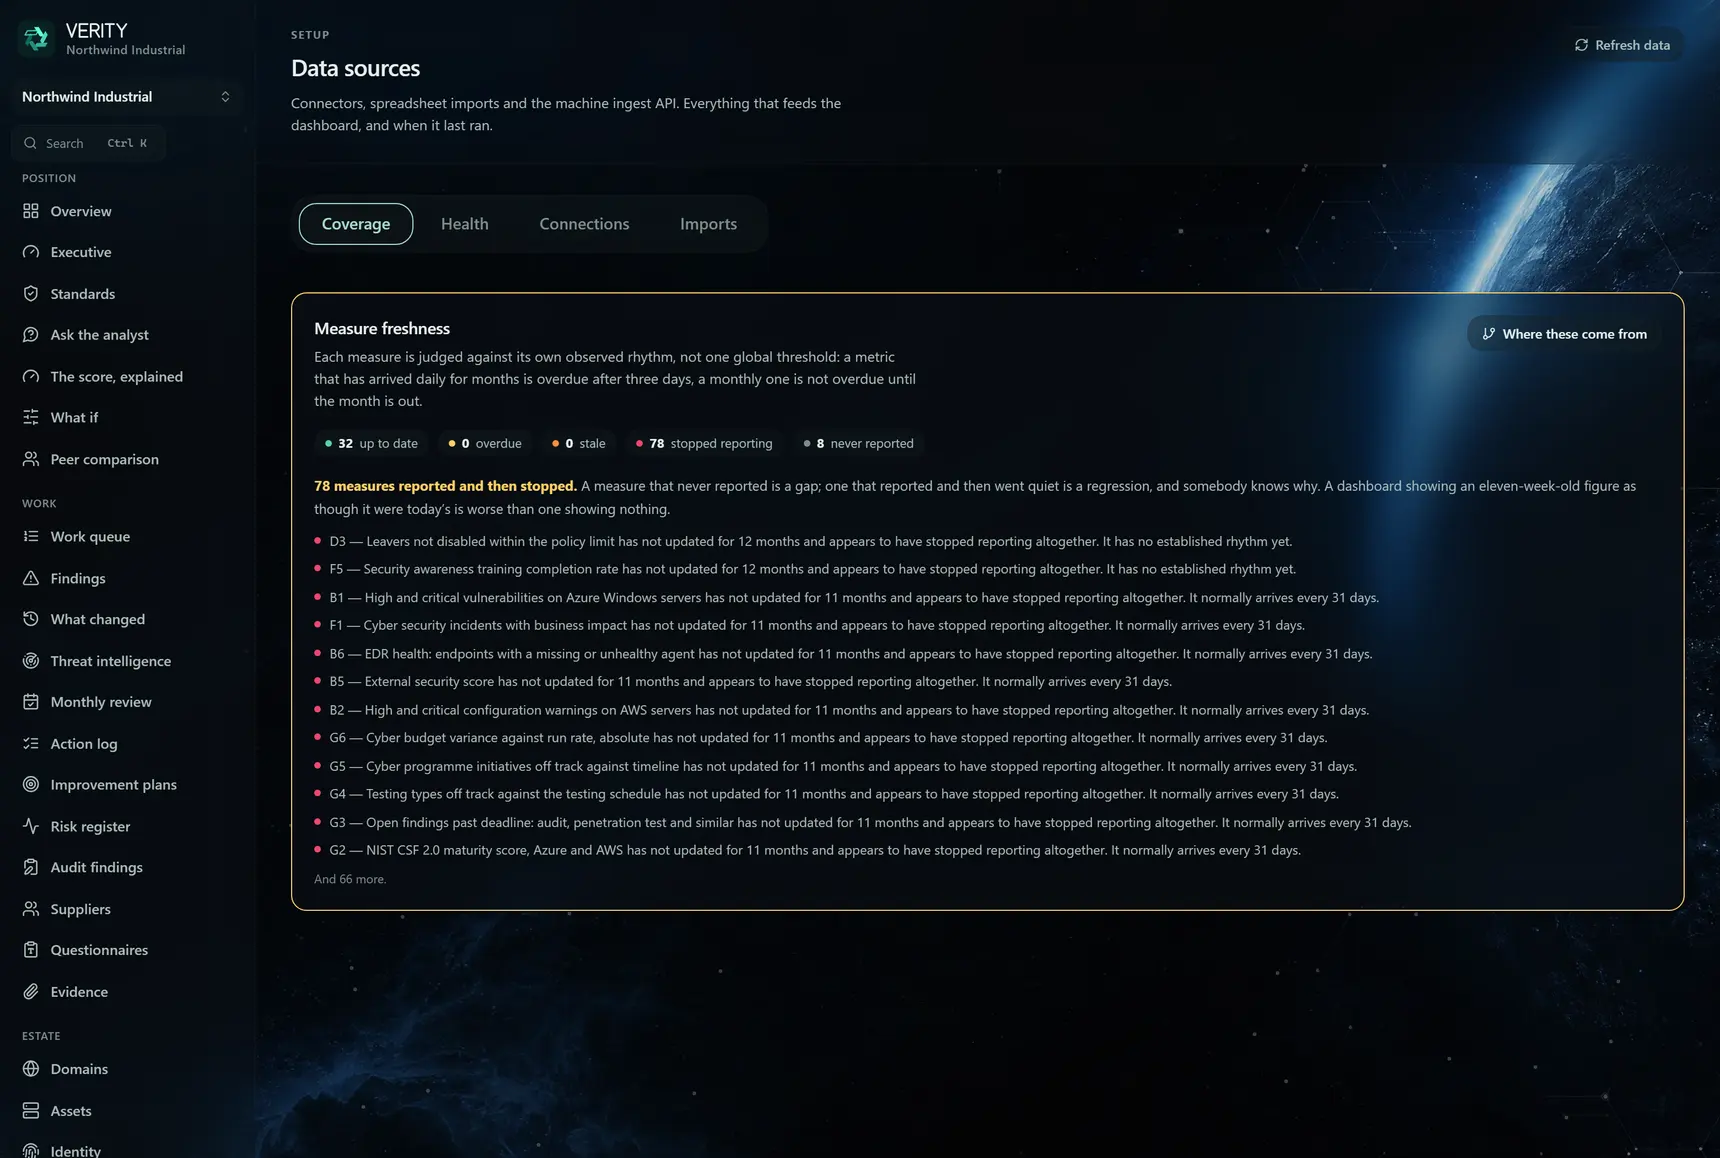
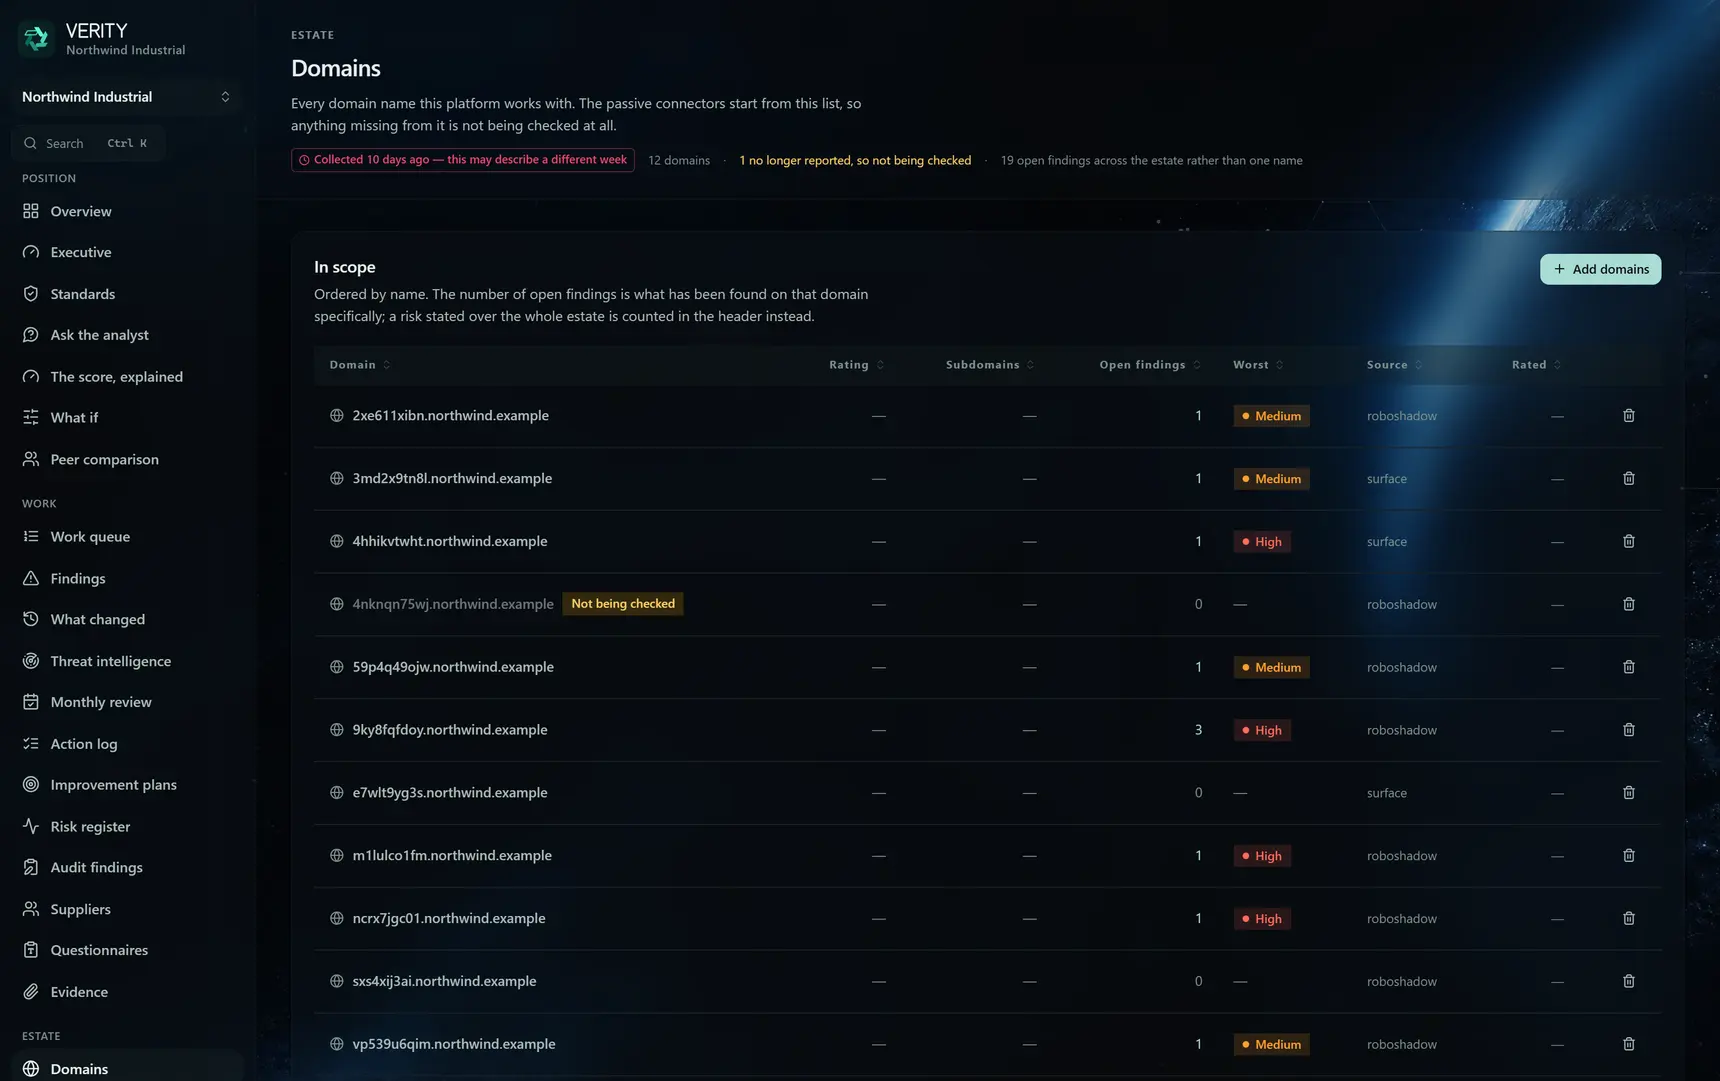
Establish what the estate can prove.
Start with source health and scope. Verity shows what reported, what stopped and which assets are actually inside the assessment boundary.
ASSESS
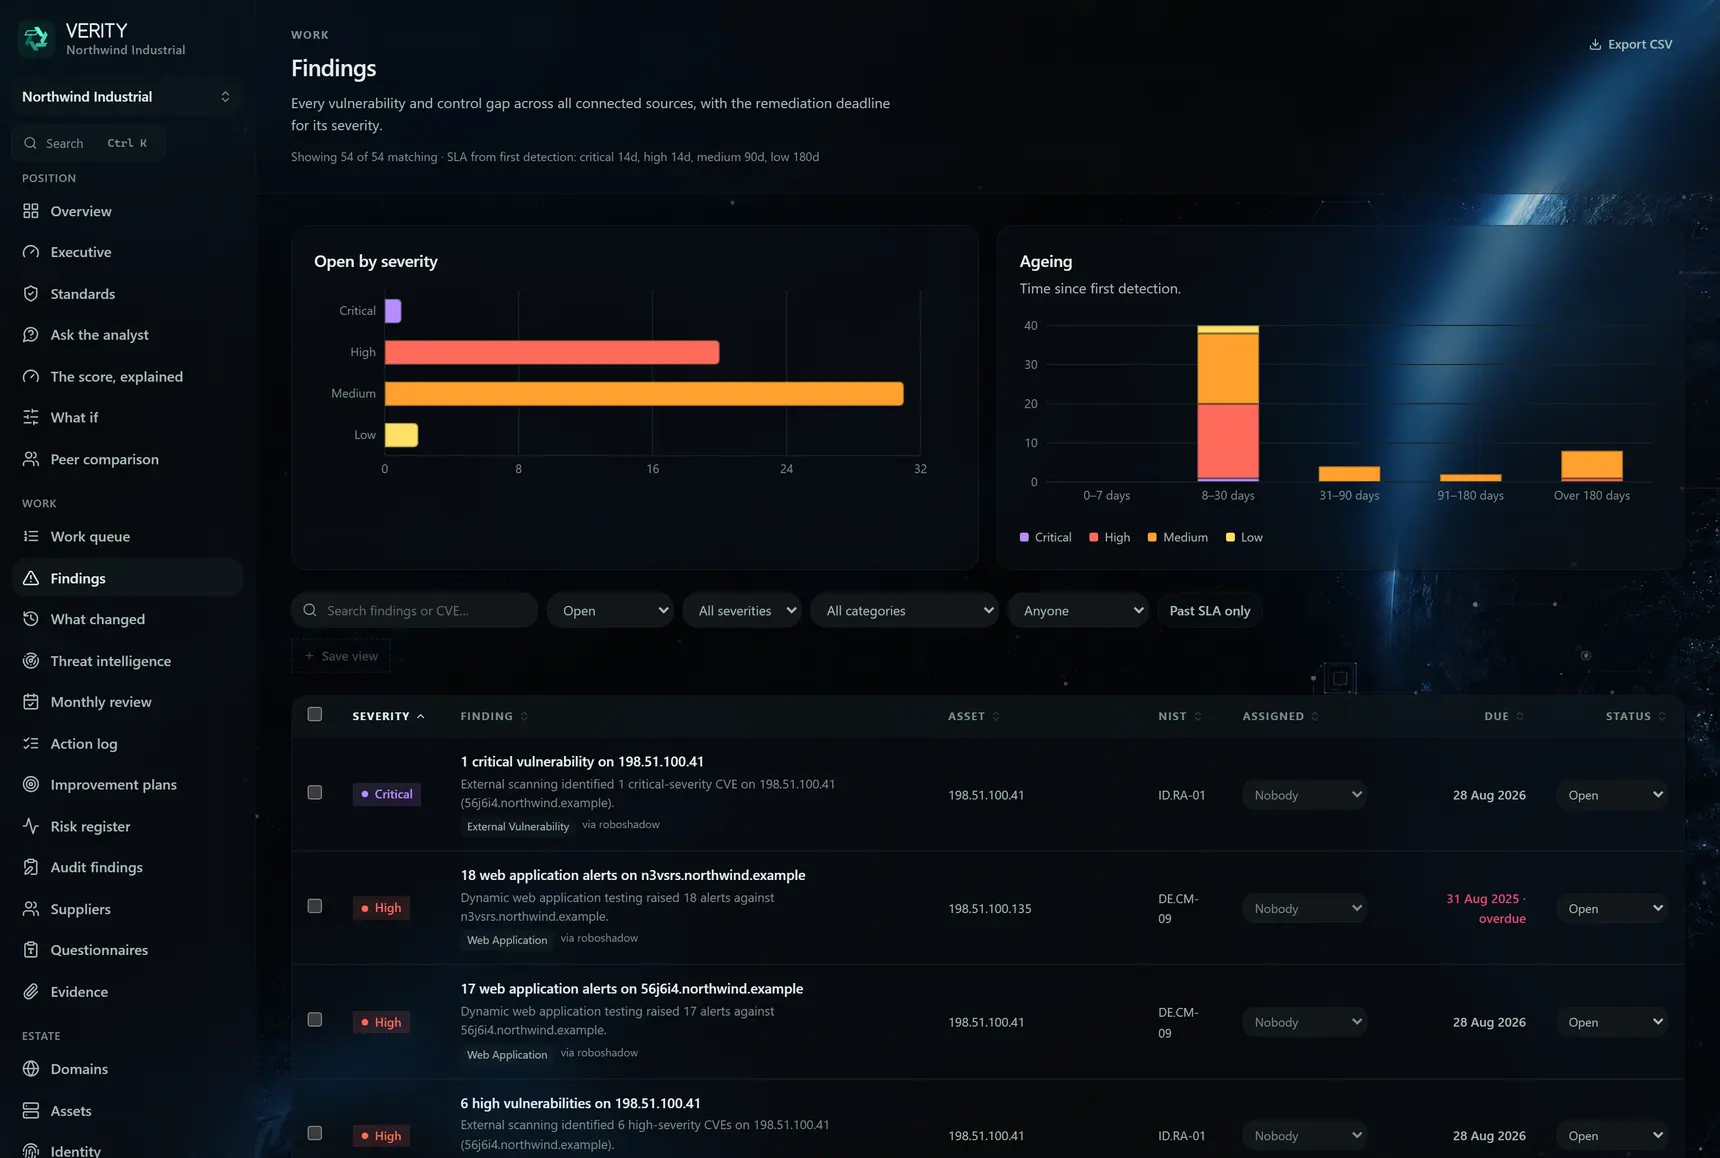
Read the position, and the pressure behind it.
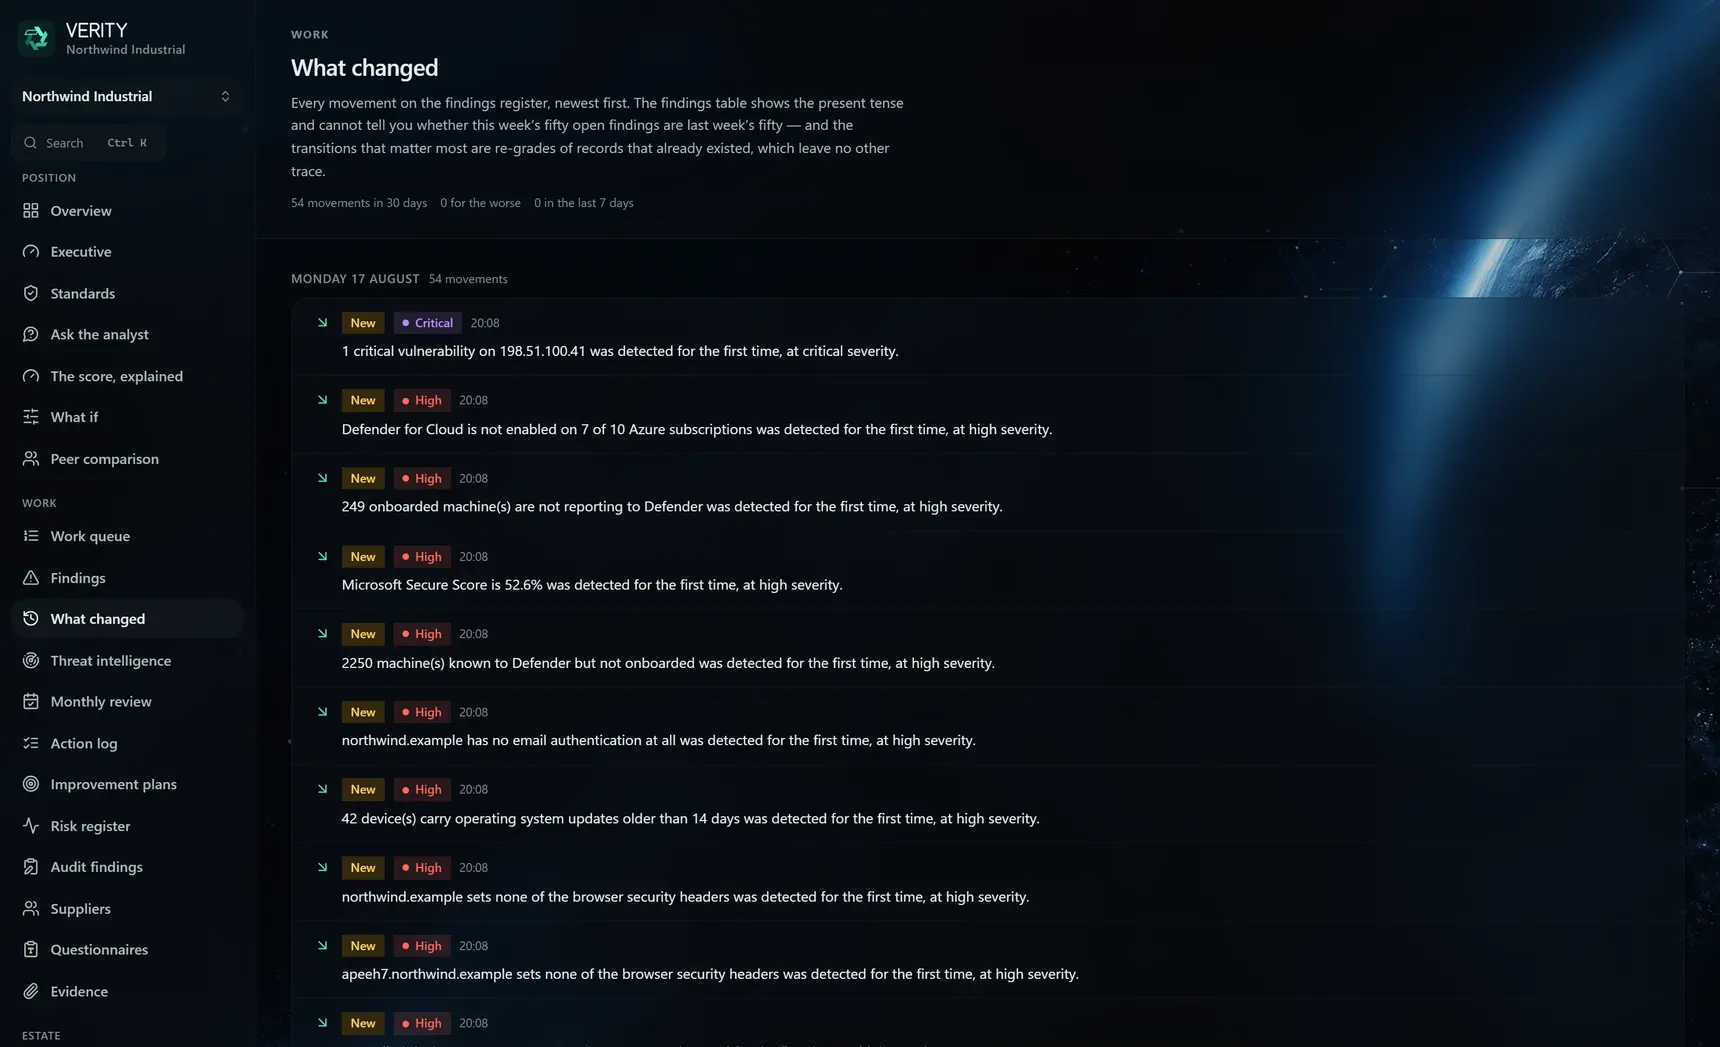
Live findings show where risk is accumulating. Readiness separates assessed controls from unanswered questions. The executive view turns both into a position the board can use.
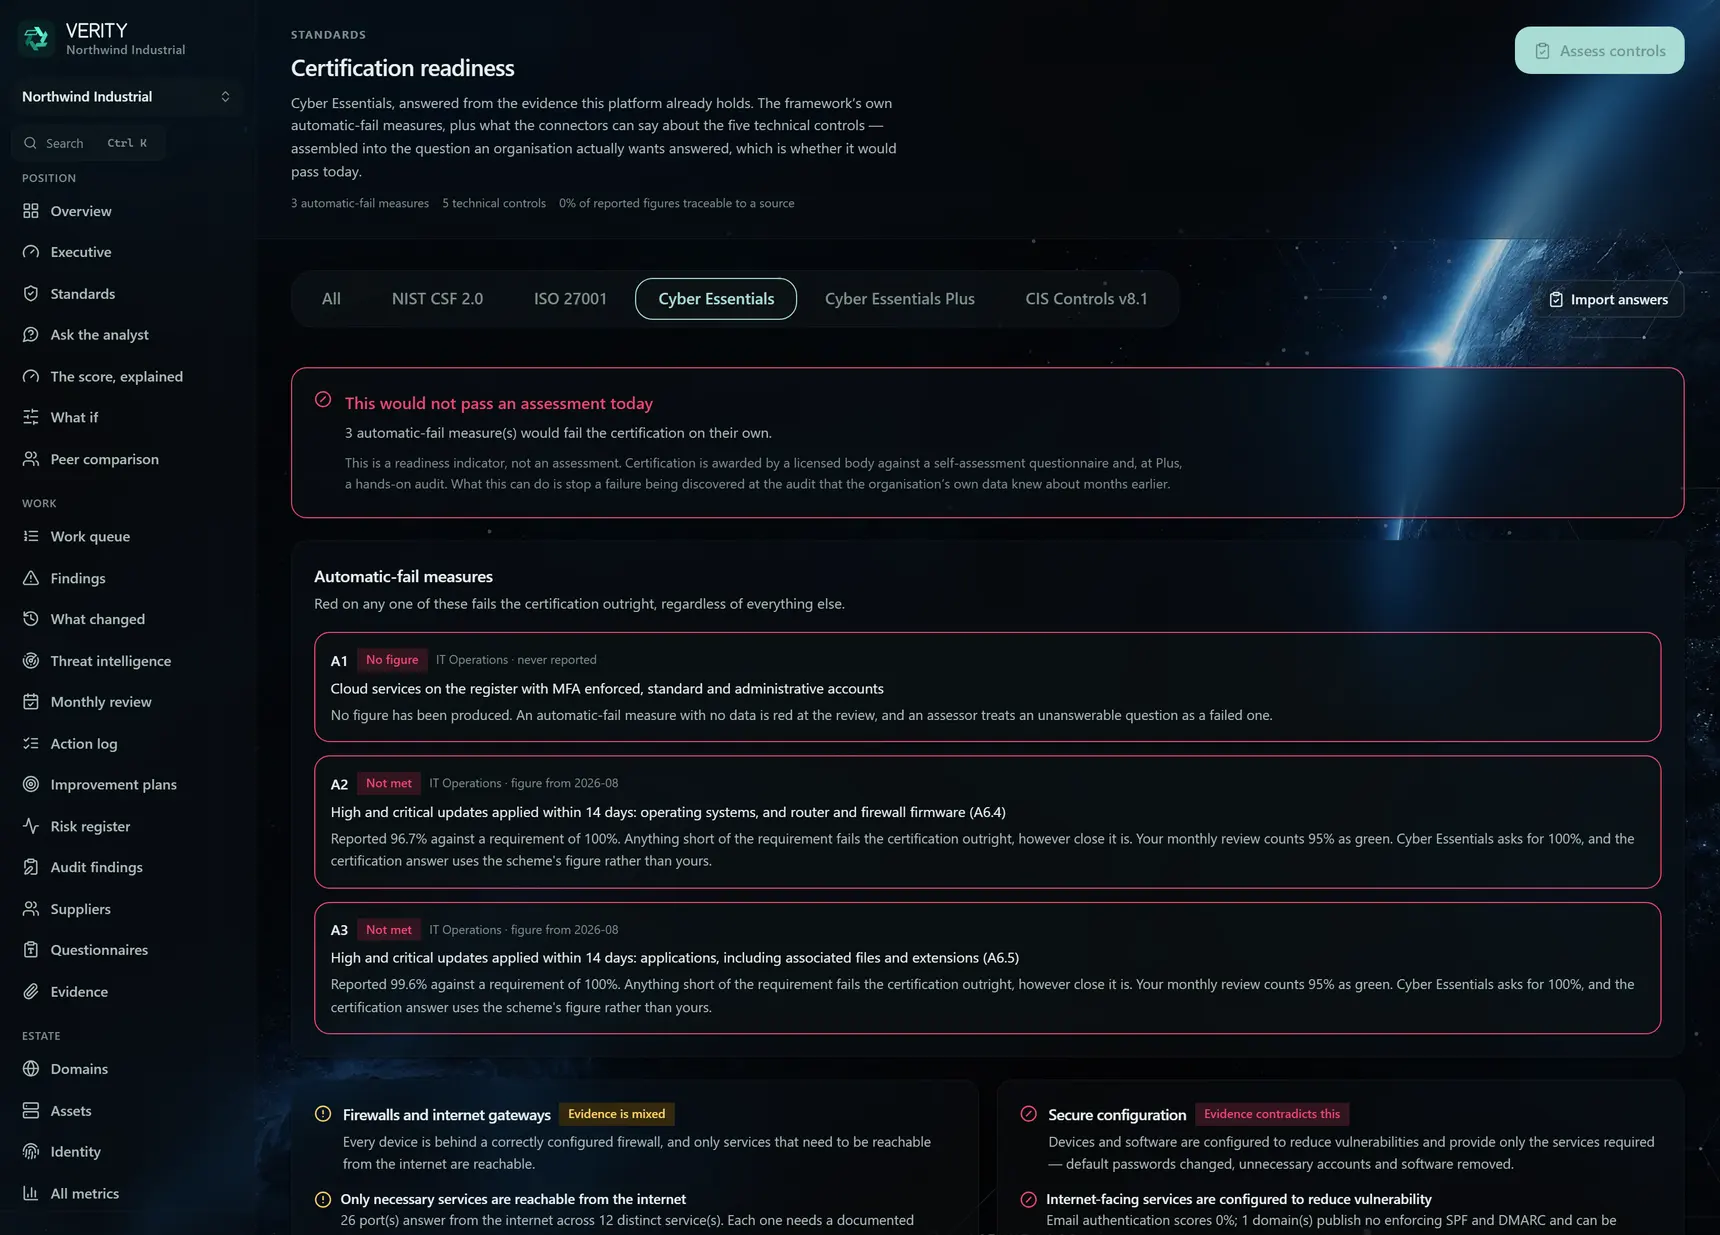
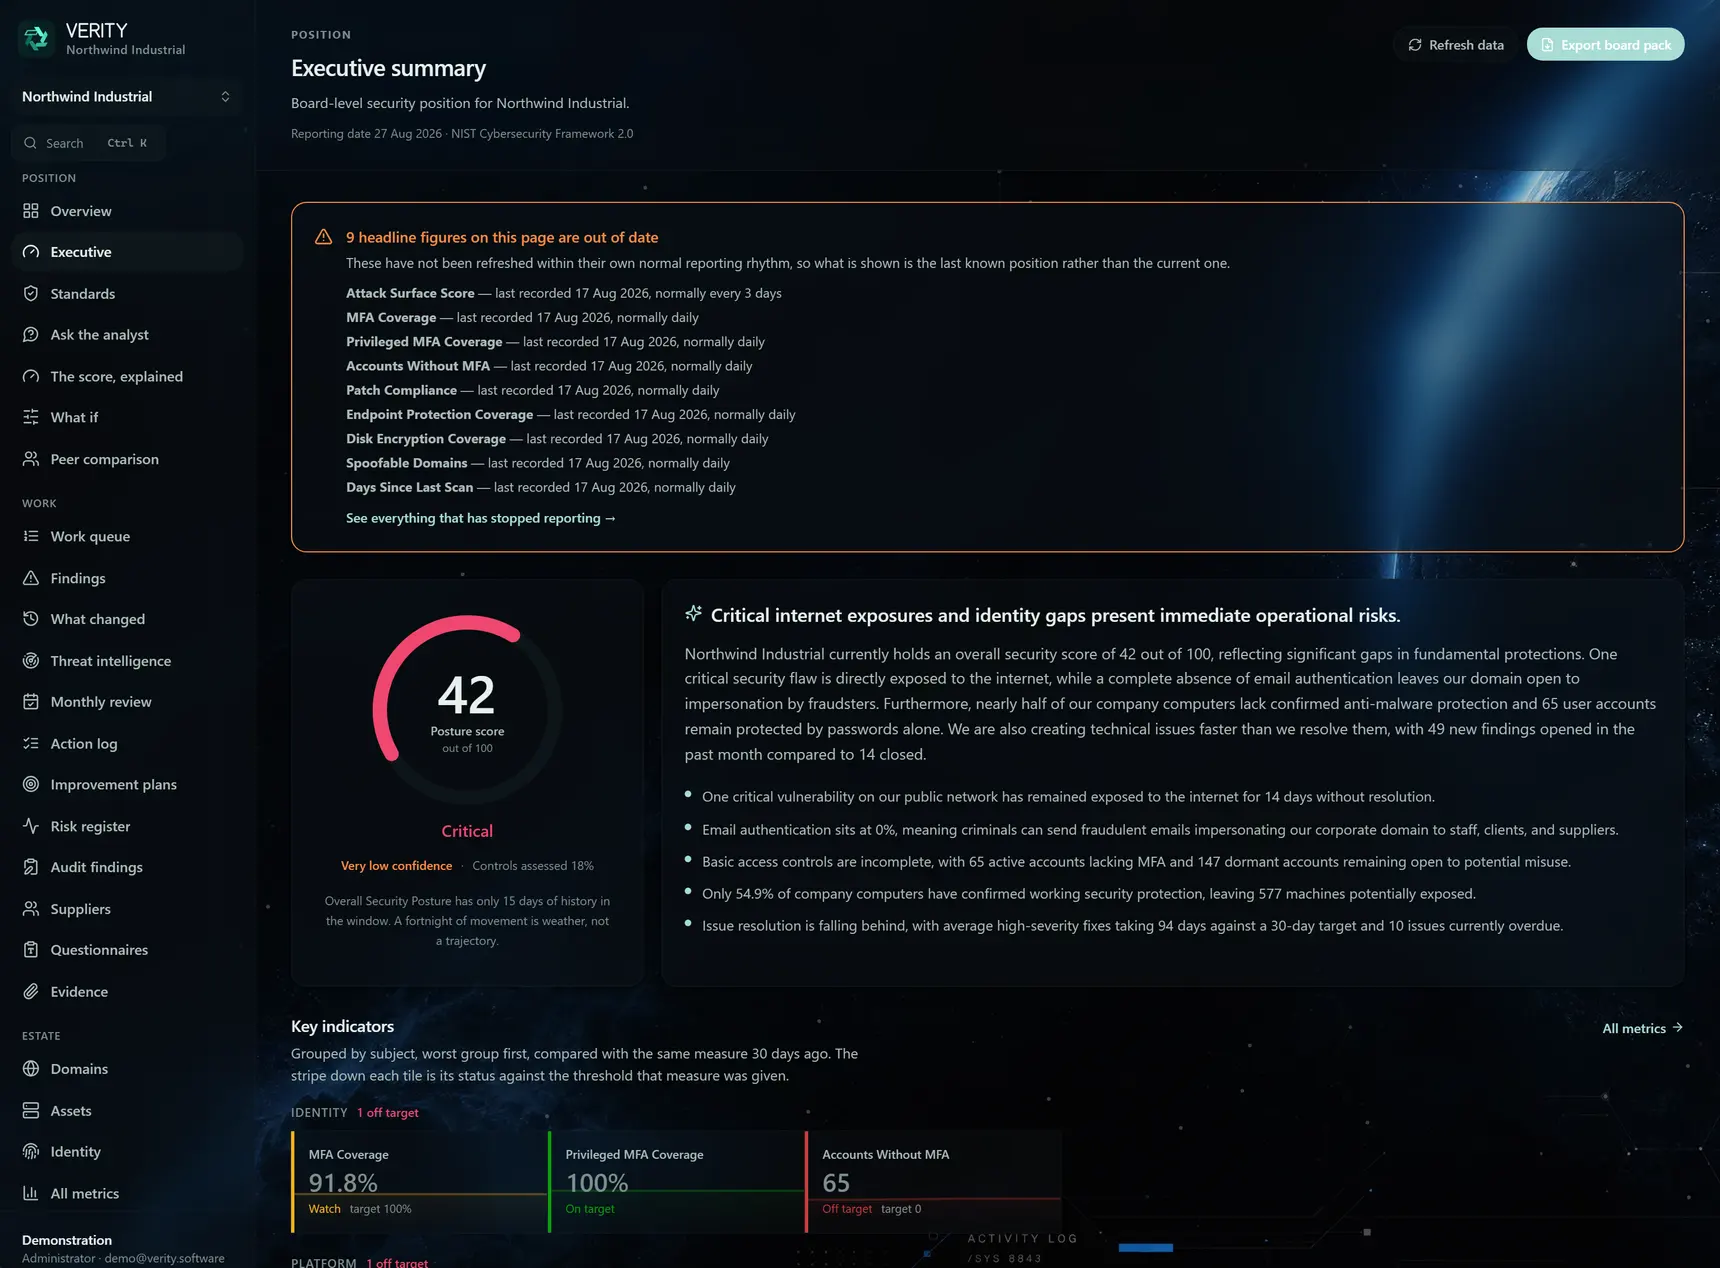
ACT
Interrogate the evidence, then test the next move.
Ask an operational question and inspect the rows behind the answer. Then run the real scoring model against proposed work, before the team commits effort to it.
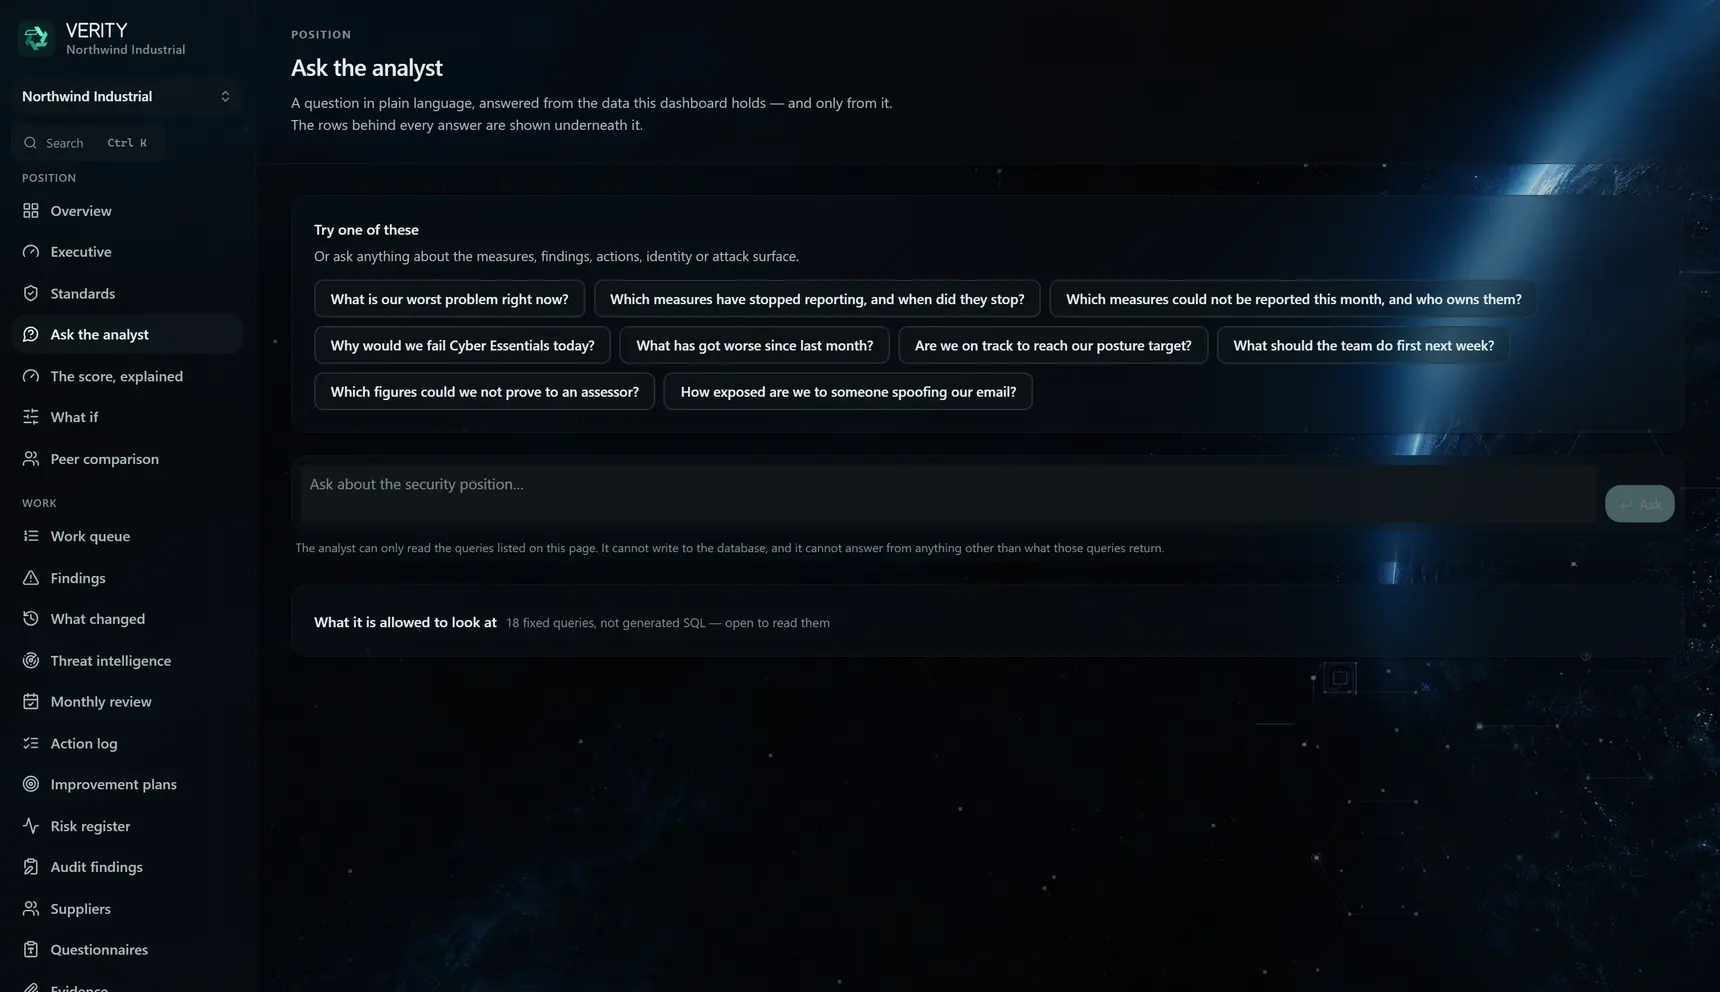
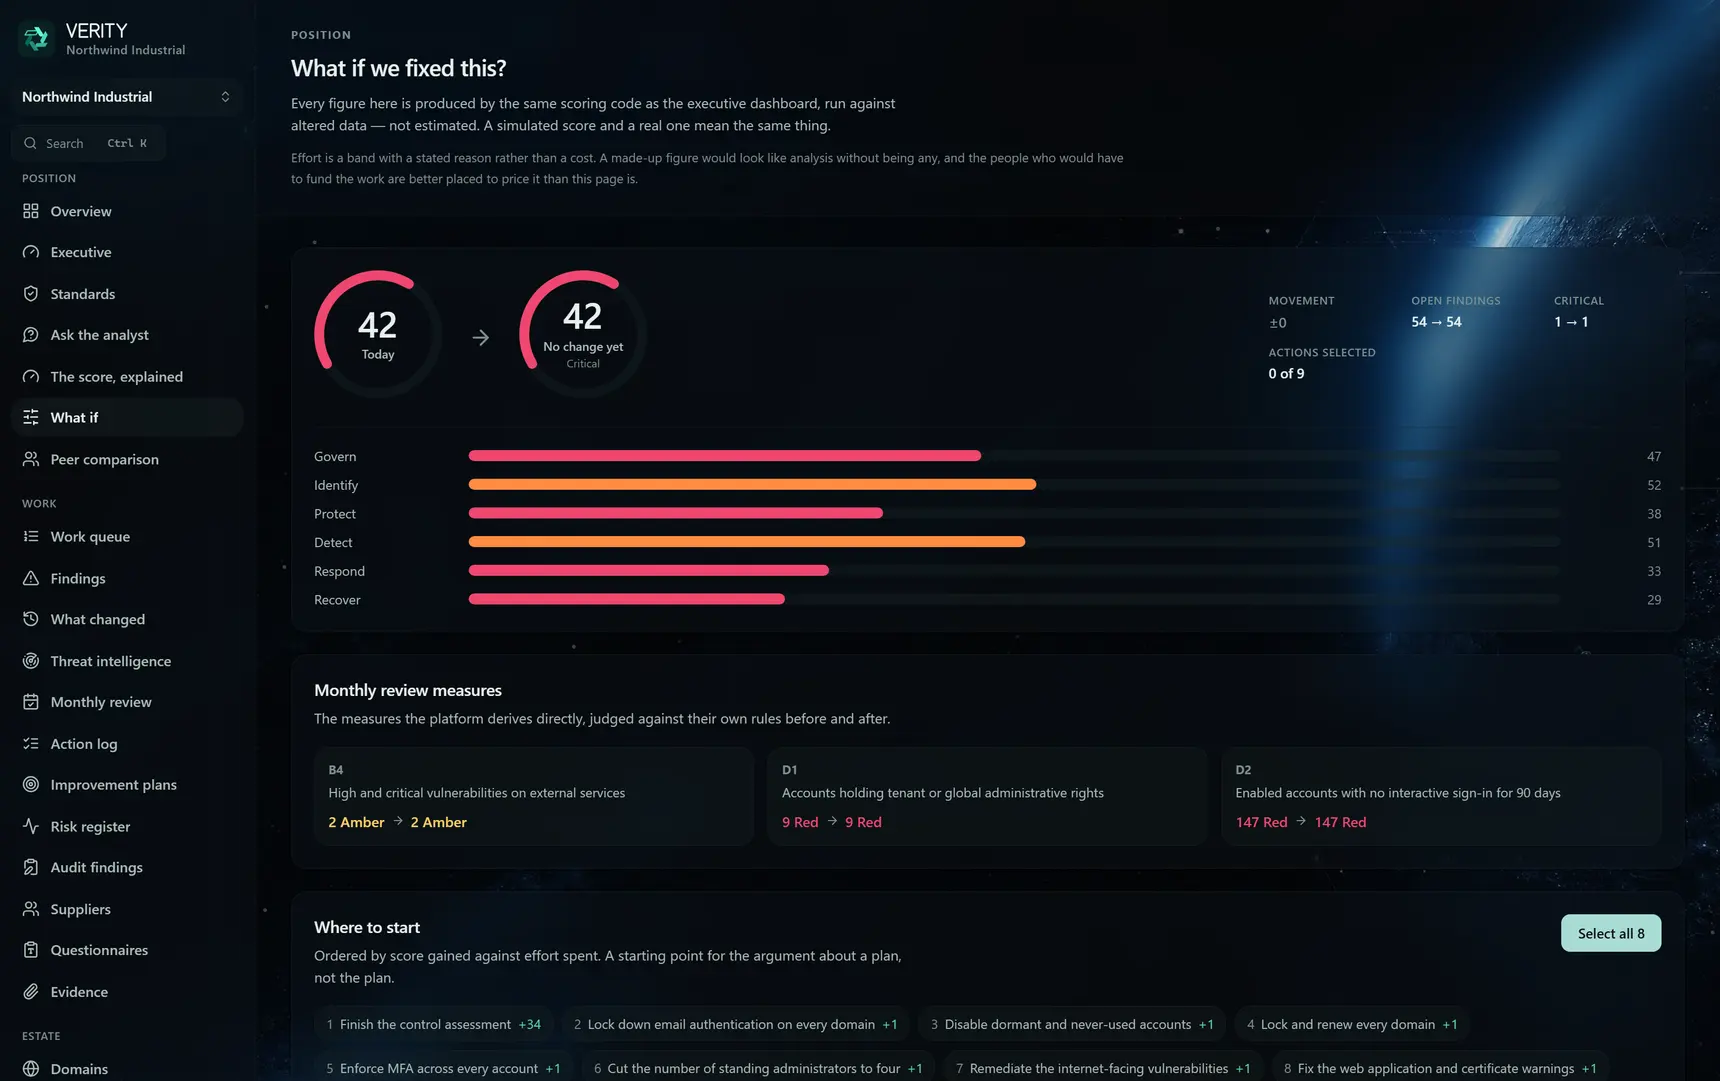
03 / OPERATIONS
Start with the whole position. Follow any figure back to its source.
The overview gives security leaders a clear reading of posture, confidence and movement. Analysts can move directly from a score to the measure, finding and source record behind it.
- Defined measures with history and ownership
- Source health and last successful sync in view
- Findings linked to the controls they affect
04 / STANDARDS
Answer the control once. Use the evidence wherever it applies.
Verity maps the same underlying evidence into every standard you are held to. Each framework keeps its own judgement model, ruleset and reporting language.
Review standards coverage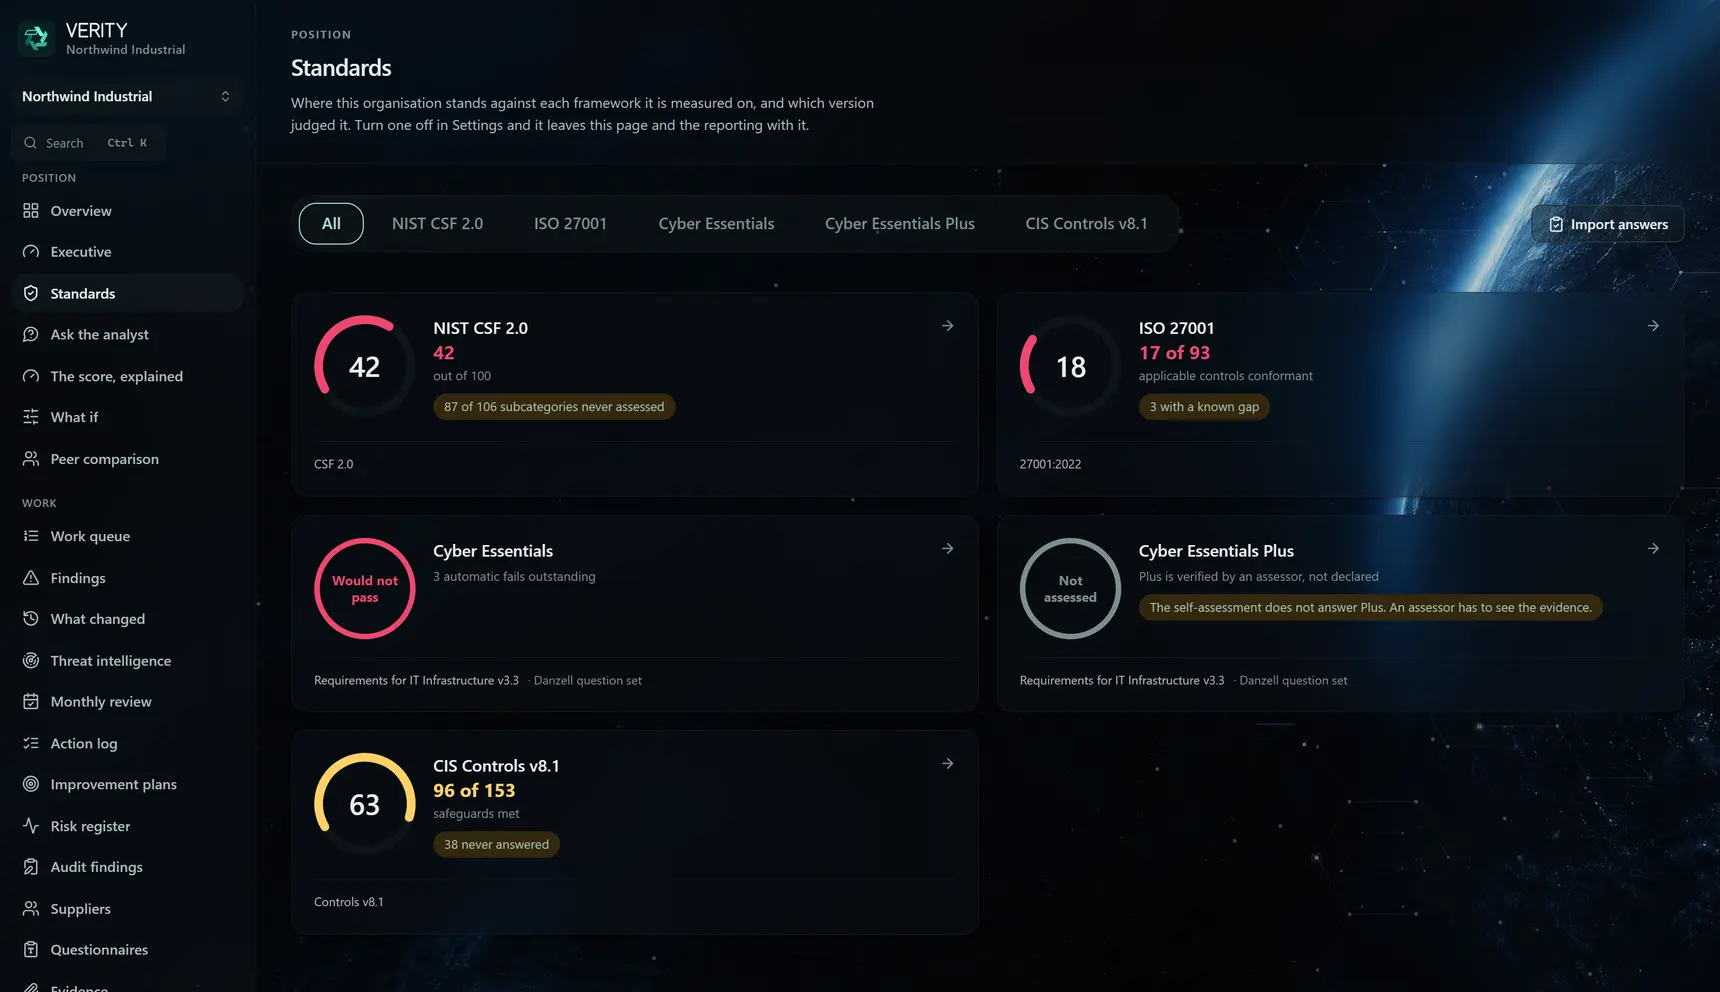
05 / THIRD PARTIES
A blank row on a supplier register is not evidence that anybody has looked.
Verity rates a supplier on what they publish rather than on how they describe themselves: mail authentication, transport, response headers, DNS controls and the front page any visitor sees. A source that answered and found nothing is a result. A source that did not answer is not.
- Vulnerabilities published against their addresses, ordered by what is being exploited now
- Names published beneath their domain, and other domains carrying their brand
- Names a stranger could claim, and domains registered to be mistaken for theirs
- What moved since the last read, limited to decisions somebody made
06 / REPORTING
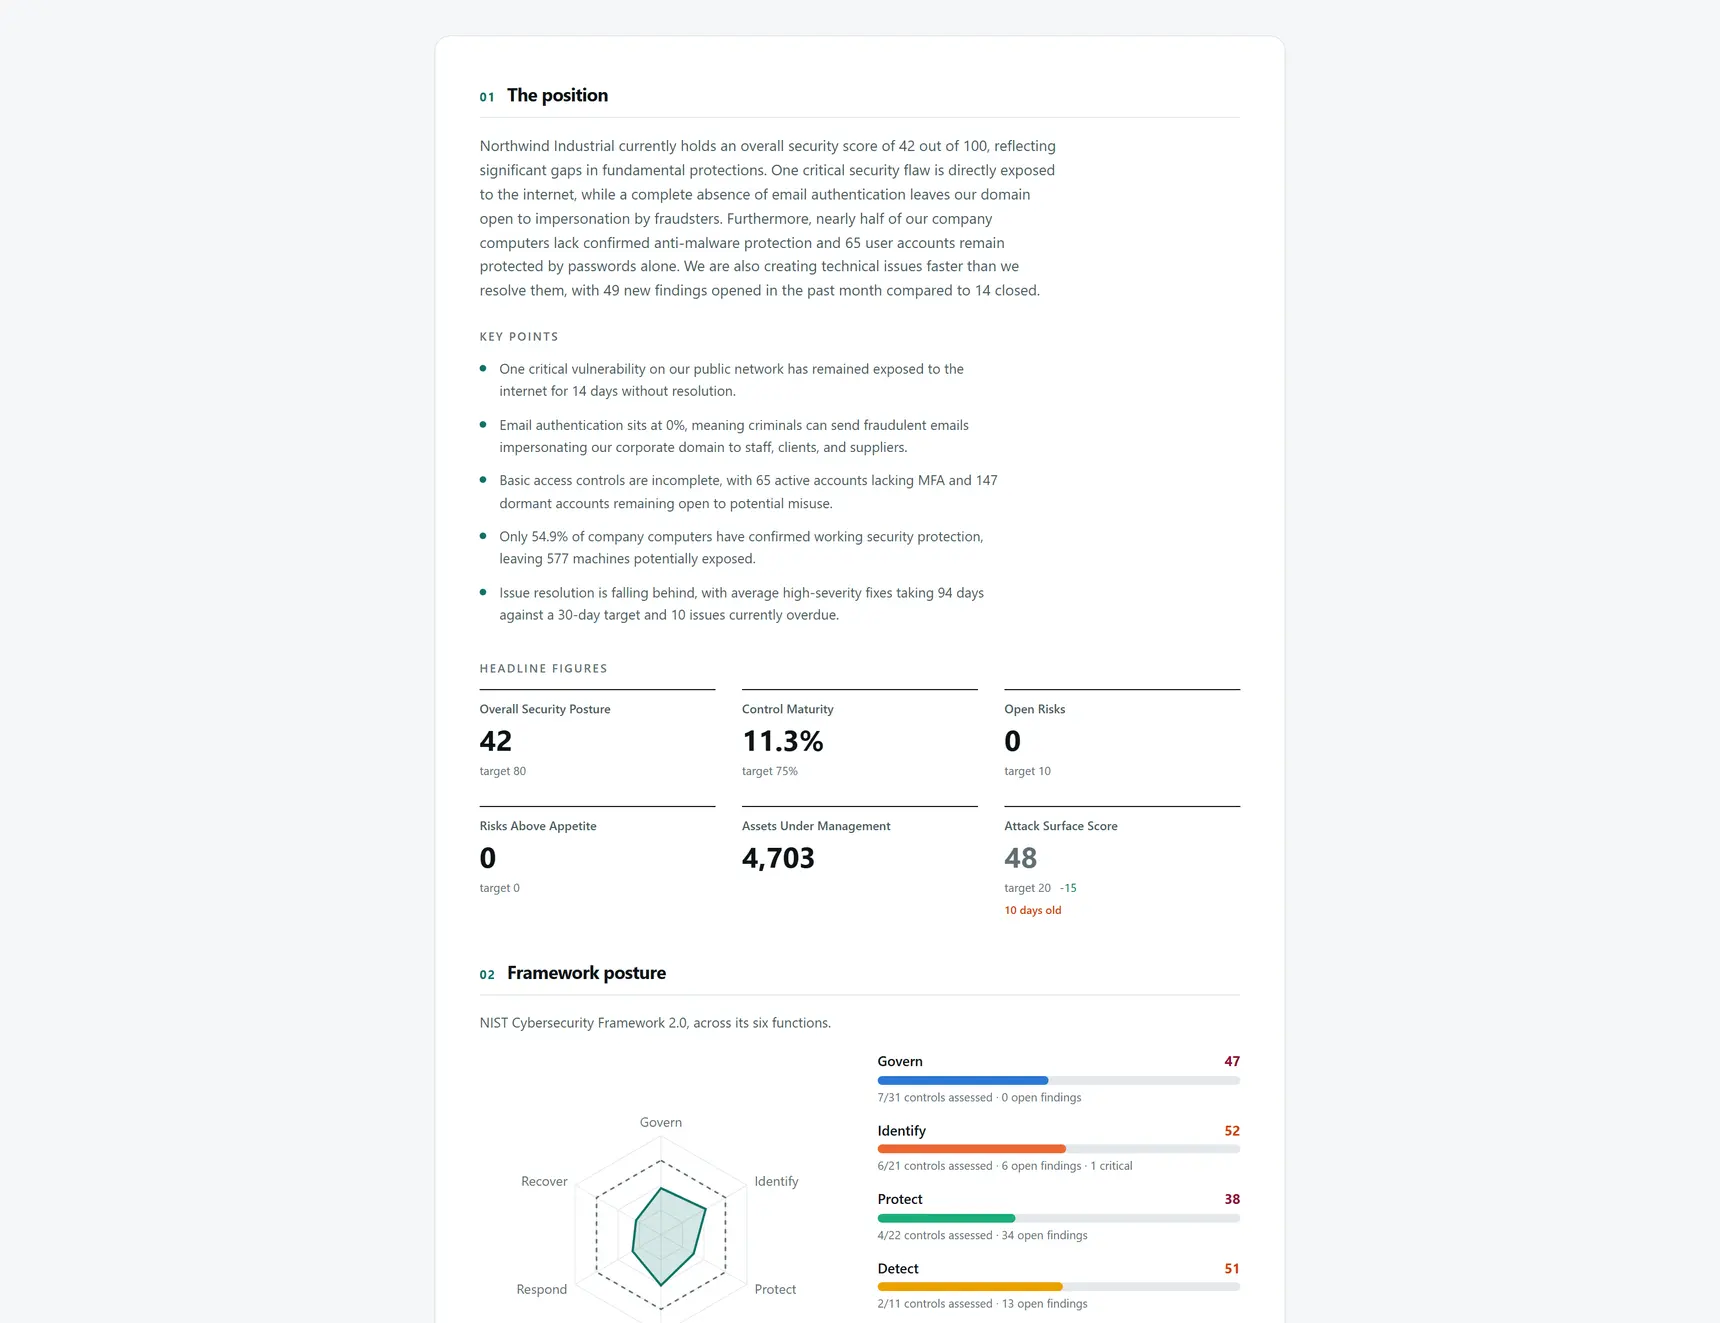
Give each audience the level of detail it needs.
Board, compliance and security reports are produced from one month's frozen evidence. The executive summary carries the decisions. The appendix carries the source trail.
07 / SERVICE PROVIDERS
A consistent view across every client estate.
Use the same measures and assessment rules across the book, while keeping each organisation's evidence, credentials and reports separate.
- See where attention is neededCompare client posture and open findings without inventing a portfolio average.
- Onboard with evidence on day oneThe passive sources can start without client credentials.
- Keep access scopedRoles and row-level controls separate each client estate.
08 / SECURITY
Designed to observe your controls, not operate them.
Verity requests the narrowest useful permissions and uses read-only access wherever the vendor provides it. Credentials are encrypted per organisation, and one client's sources remain isolated from another's.
SEE IT WITH YOUR OWN EVIDENCE
Know where you stand before the next board or audit asks.
Connect one source and review what Verity can measure, what it cannot, and what should happen next.
Request a working session