01 / COVERAGE
Answer it once. Satisfy every standard it touches.
Record that privileged accounts hold a second factor and you have moved NIST PR.AA-03, ISO 27001 Annex A 5.17 and the Cyber Essentials access control at the same moment. Nobody answers the same question three times because it carries three reference numbers.
02 / SCORING
Assess more of the programme and the number can fall.
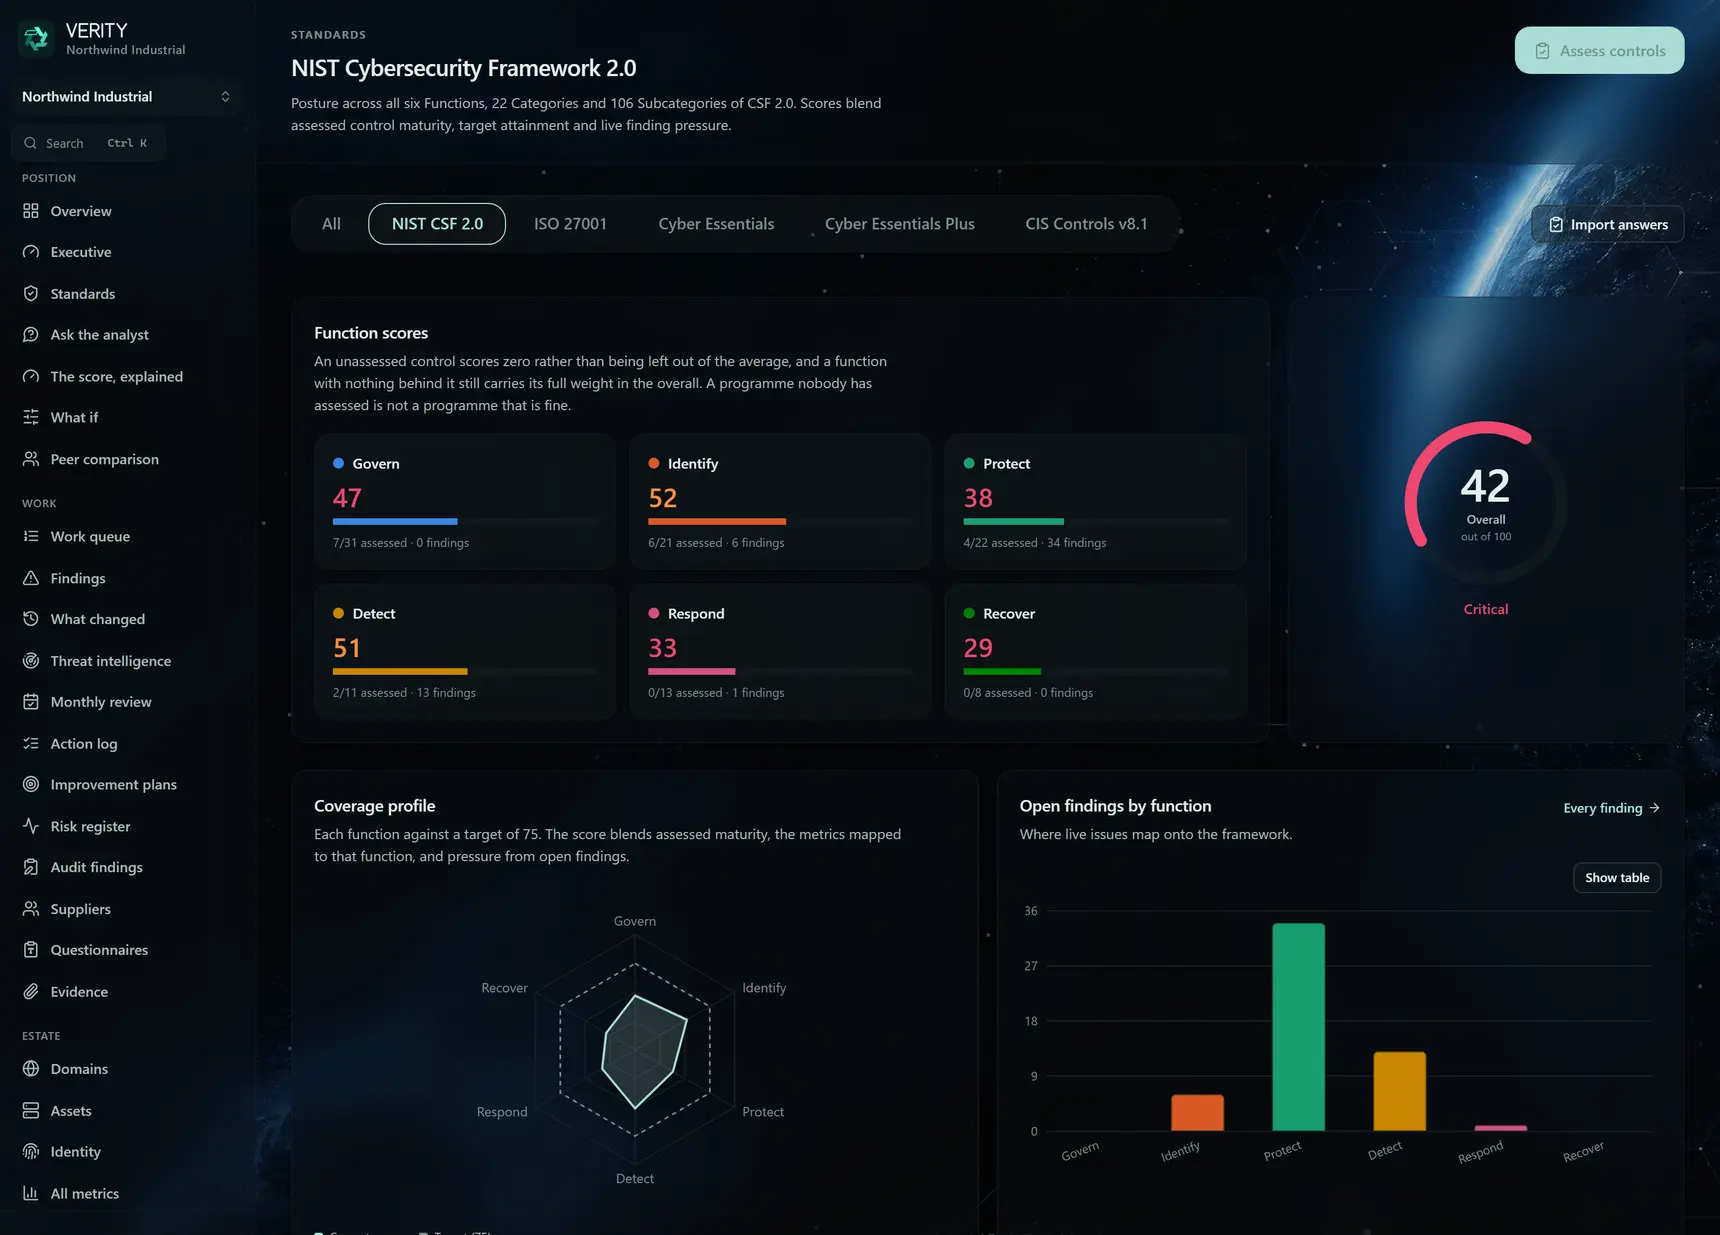
An unassessed control scores zero and stays in the denominator. It is not set aside until somebody looks at it, so the score carries the unanswered questions rather than the average of the answered ones.
A vulnerability arriving can never raise a function score. Finding pressure only scores where collection has demonstrably run, so an empty result is an absence of evidence rather than a clean estate.
03 / READINESS
Would you pass today, and what has nobody looked at?
Every readiness answer carries a panel headed what this cannot see. Not in a footnote: on the screen, beside the answer, in the same size type.
Whether the boundary firewall's default password was changed. Whether the management interface answers from the internet. Host firewall state where no agent is reporting. That list is the assessor's question list, months early.
How Verity itself is secured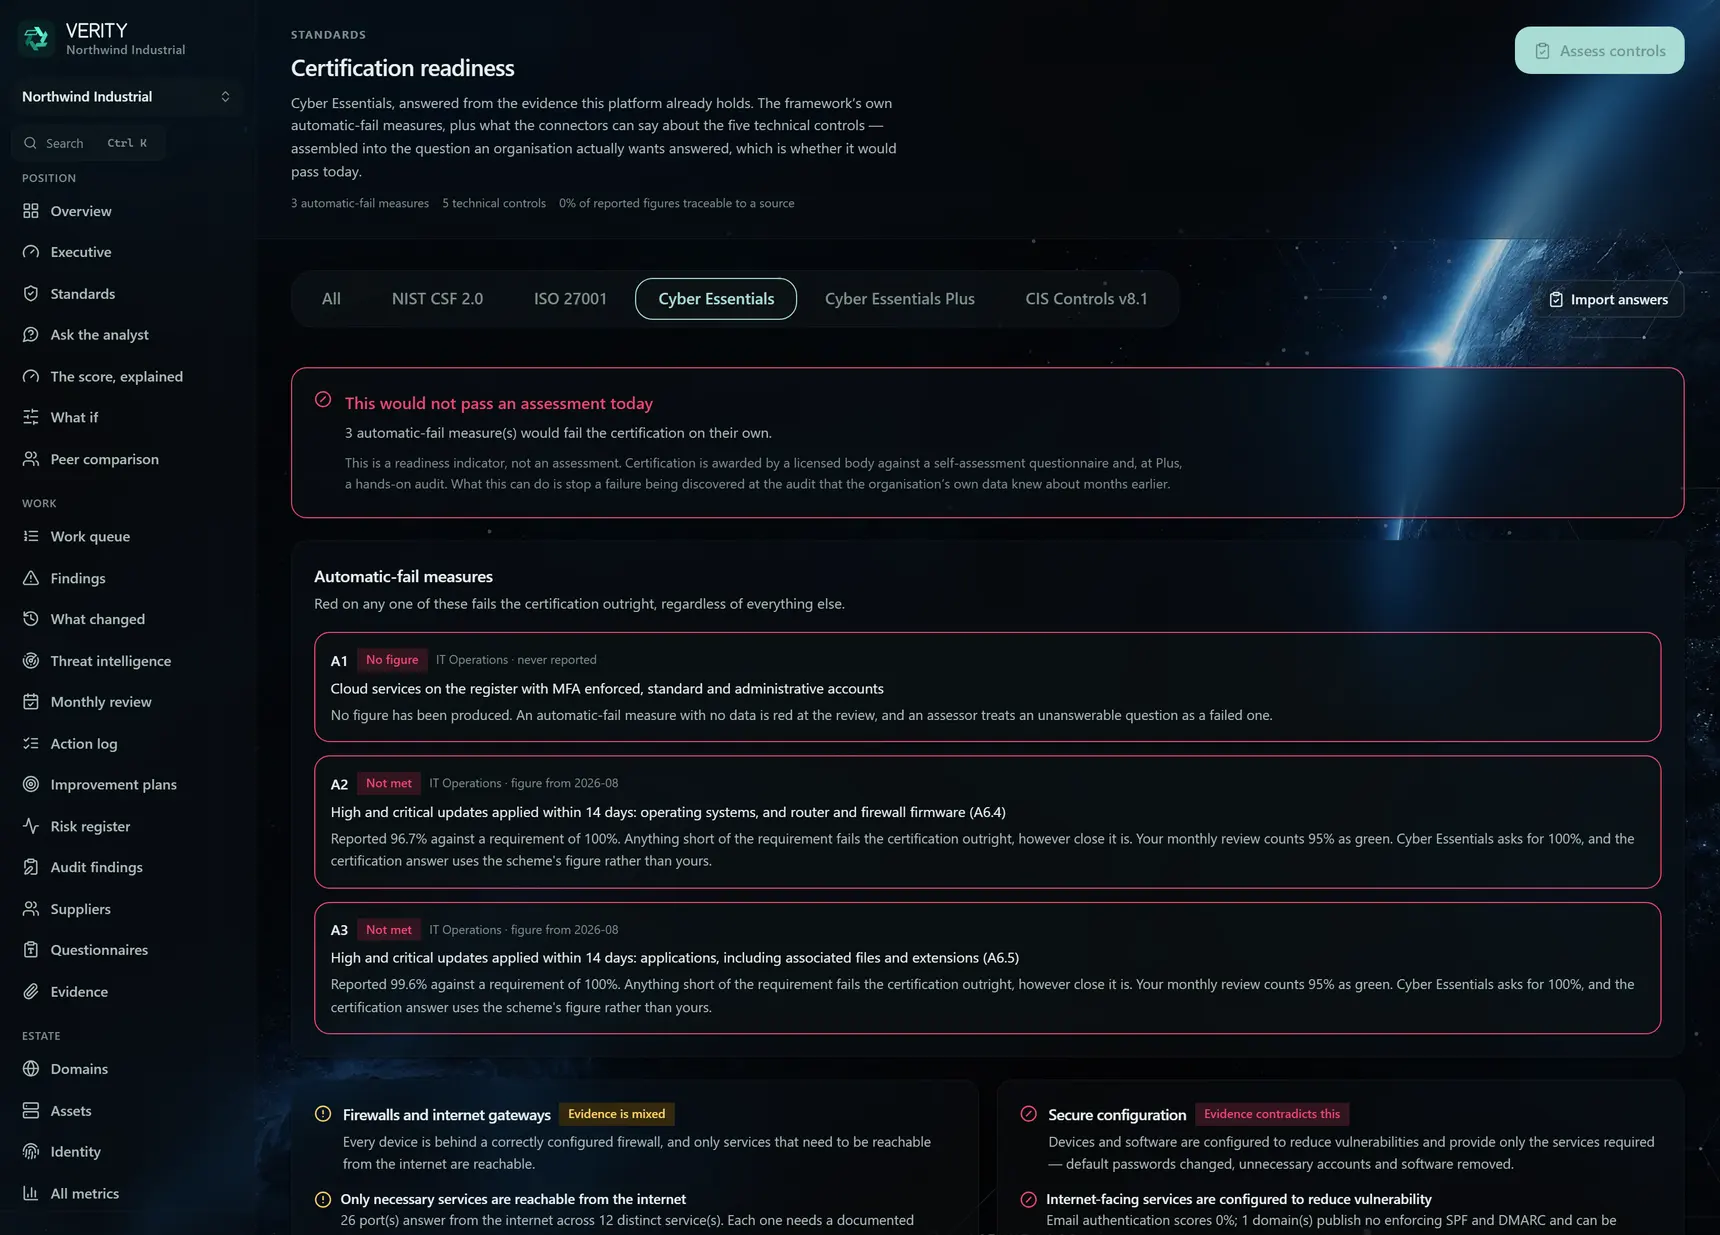
04 / LIMITS
What none of this is.
- Not a certificationCyber Essentials and CE Plus are awarded by a licensed body, ISO 27001 by an accredited auditor. Verity tells you where you stand before you go, and cannot award anything.
- Not the schemes' own wordsEvery catalogue is written for this product because the source text is licensed. The numbering is theirs; the wording is ours.
- Not connected to anybodyVerity does not submit to, file with, or exchange data with NIST, ISO, IASME, NCSC, CIS or the Bank of England. Every score is computed from your own data.
- Not an opinion on everythingTelemetry cannot answer governance, training and process controls. Those are recorded as assessed by a person, or left unanswered.
BEFORE THE ASSESSOR ASKS
Find the gap while there is still time to close it.
Connect one source and look at what comes back, including the parts it says it cannot see.
Request a working session